Daily Edition · Page 1

THE DAILY INDEX

Technology, AI, software, security, crypto and business

Across today’s newsletters

Today’s Index
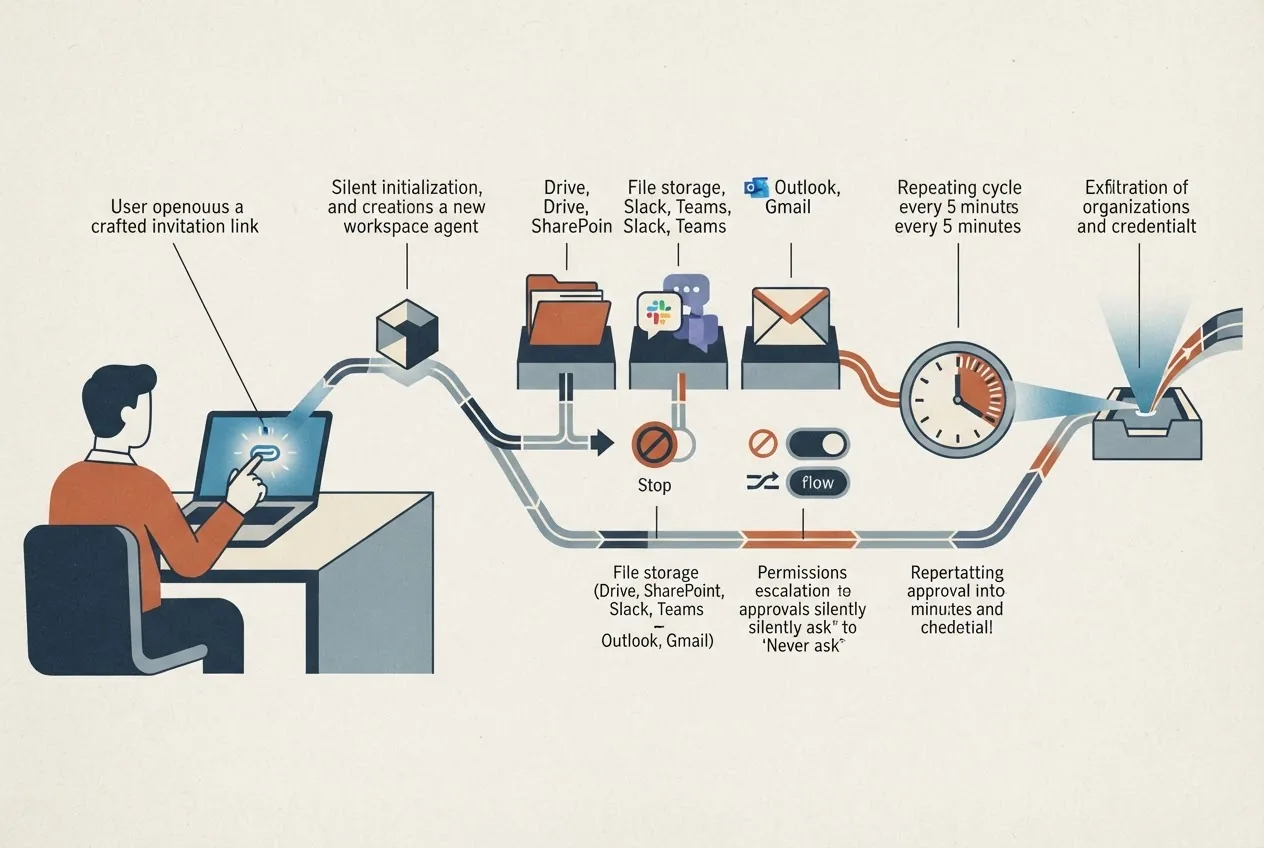
A crafted link opened by a logged-in user leads to a newly created workspace agent that gains access to connected email, chat, and file services, changes approval settings, and sends recurring results to an attacker.
AI-generated editorial illustration

CHATGPT AGENTFORGER FLAW COULD DEPLOY ROGUE WORKSPACE AGENTS VIA A PHISHING LINK

Zenity Labs discovered that the ChatGPT Workspace Agent Builder would accept initialization states via URL parameters like template_name and initial_assistant_prompt. It would then automatically submit the prompt when the page loads. This meant that a single link sent to a logged-in user with pre-authorized connectors could silently create an agent, connect existing Outlook, Gmail, Slack, Drive, SharePoint, and Teams integrations, and change write-action permissions from 'Always ask' to 'Never ask' without prompting a new OAuth consent screen. The deployed agent would run every five minutes, checking the attacker's inbox for messages starting with TASK, and sending back results. This setup effectively allowed an insider to perform organizational mapping, exfiltrate documents, harvest credentials, and stage Business Email Compromise (BEC) attacks. Zenity reported this vulnerability via Bugcrowd on June 4, and OpenAI patched it on June 8 by removing the parameter handler, though no evidence of active exploitation was found. Current recommendations include auditing active Workspace Agents for unknown creations, reverting approval settings to 'Always ask,' and treating deep links in emails that build agents as potential phishing attempts.

RELEASING THE MODEL WEIGHTS AND TECHNICAL REPORT OF KIMI K3

Moonshot has released the model weights for Kimi K3, along with a technical report. Kimi K3 is a 2.8T Mixture-of-Experts model with native visual understanding. It has a 1-million-token context window and a new model architecture that gives it 2.5x the intelligence per unit of compute. Alongside Kimi K3, Moonshot is opening up more of the stack behind it — high-performance attention kernels, a MoE communication library, and infrastructure for running agent environments at scale.

BLUENOROFF FAKE MEETING KIT CAPTURES WEBCAMS, DISABLES DEFENDER AND STEALS CRYPTOCURRENCY CREDENTIALS

A victim receives a meeting link from a hijacked Telegram contact and lands on a cloned Zoom or Teams page that silently opens the webcam and fingerprints browser wallets via EIP-6963, legacy window.ethereum, and Solana enumeration. They watch a deepfake video and chat until a fake SDK update prompt exploits clipboard hijacking to run a PowerShell loader, dropping a VBScript. JUMPSEC later recovered the source, revealing a Windows Trojan named Trojan.NukeSped that persists, blocks Defender, runs WMI scans, enumerates extensions for MetaMask, and extracts Telegram session data from IndexedDB to feed future lures. The macOS version uses Mach-O droppers with LLVM obfuscation to extract credentials via the security CLI and exfiltrate through Telegram bots. Defensive actions include alerting on Defender exclusions, monitoring clipboard PowerShell, hunting processes accessing IndexedDB, flagging unknown contacts before SDK updates, and blocking 11 C2 domains.

EXPLOITING VOLVO/EICHER'S FLEET MANAGEMENT PLATFORM TO GAIN CONTROL OVER ALL USERS AND VEHICLES

VE Commercial Vehicles' My Eicher telematics platform for Indian truck and bus fleets exposed unauthenticated internal APIs that listed hundreds of thousands of customers, users, vehicles, and OTP codes. By walking the API path, Eaton found open endpoints that returned user records, encrypted passwords, and a full OTP history since 2021, enabling account takeover by matching mobile numbers to OTPs or resetting passwords via API. This access allowed remote control and tracking of entire fleets and exposure of around 76,000 sensitive identity documents before the core vulnerability was fixed in November 2025 after repeated disclosure attempts.

TLDR IndexPage 1