Daily Edition · Page 1

THE DAILY INDEX

Technology, AI, software, security, crypto and business

Across today’s newsletters

Today’s Index
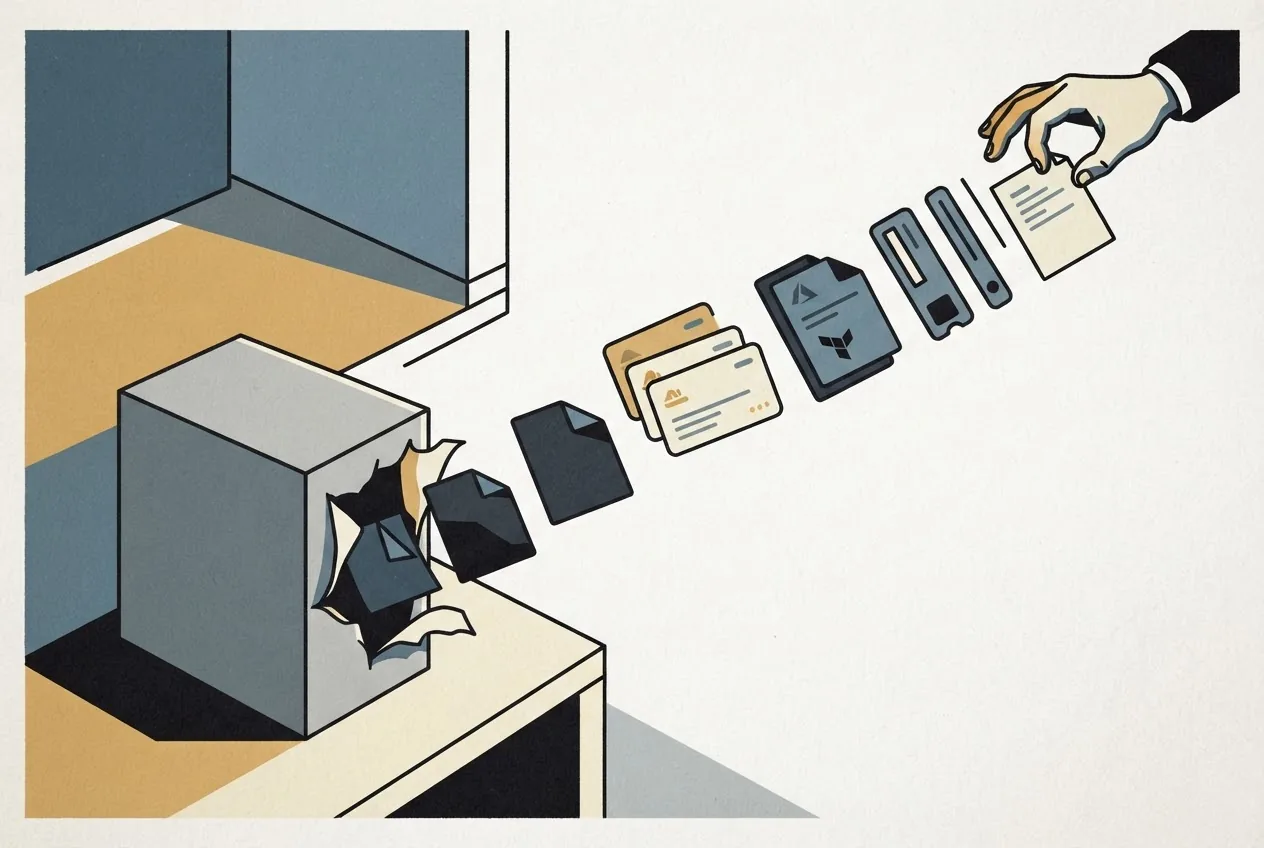
An exposed development server reveals project files and cloud credentials through a breached boundary, illustrating how attackers can escalate from a Vite flaw to sensitive infrastructure data.
AI-generated editorial illustration

MASS-SCANNING CAMPAIGN EXPLOITS VITE FLAW TO EXTRACT CLOUD CREDENTIALS FROM EXPOSED DEV SERVERS

Attackers scanned exposed Vite development servers in August and exploited CVE-2026-39364. Crafted query parameters bypassed server.fs.deny and returned protected files through /@fs/. Observed targets included .env files, AWS credentials, Azure profiles, Terraform state, database passwords, and /proc data with requests spoofing crawler user agents and forged forwarding headers.

META LAUNCHED AN AI THAT USES WEBSITES FOR YOU. THAT COULD BE A BIG DEAL FOR WEB DESIGNERS

Meta launched Muse, a consumer AI agent built on its Muse Spark model that can navigate websites, fill forms, send emails, book travel, and make payments. The browser sub-agent reads an accessibility-tree snapshot of pages rather than the raw DOM, so semantic structure and accessibility may grow increasingly important for web designers. Reuters reported that internal testing found reliability problems, including an instance where an agent exposed personal iCloud photos, though Meta says added security work delayed the launch.

OPENAI CONSIDERS PRE-IPO FUNDING ROUND AT MORE THAN $1.2 TRILLION VALUATION

OpenAI has held early discussions with investors about a financing round that would precede the company's highly anticipated initial public offering expected next year. The new funding round, which could value the company at more than $1.2 trillion, has been delayed due to concerns about AI safety. OpenAI has reached more than one billion active users, with more than 200 million businesses using its models.

DREAMFORCE 2026: SLACK'S NEWEST INNOVATIONS TURN AI INTO A TRUE TEAMMATE

Slack is expanding far beyond chat with Slackbot in channels, full-screen AI workspaces, live Salesforce-powered Surfaces, and Slack Code, where developers and AI agents can build and review code collaboratively. Slack is becoming a control surface for more business systems and agents, raising new questions around app governance, permissions, licensing, and what employees should be allowed to connect.

EU CYBER RULES PUT CRYPTO WALLET MAKERS ON 24-HOUR REPORTING CLOCK

The EU's Cyber Resilience Act took effect on September 12, placing crypto wallet manufacturers on a tiered disclosure schedule: a 24-hour early warning for severe vulnerabilities, a 72-hour full notification, and a final report due 14 days after corrective measures are available. The regulation covers all hardware and software wallet products distributed in the EU, with penalties reaching €15 million or 2.5% of global annual turnover for violations of core reporting articles, and €5 million for inaccurate or incomplete disclosures. The effective date coincides with active security events: Trezor disclosed that 67,000 US customers faced exposure from a third-party shipping breach, and both Trezor and BitBox issued phishing warnings tied to compromised email services in September.

TLDR IndexPage 1