Daily Edition · Page 1

THE DAILY INDEX

Technology, AI, software, security, crypto and business

Across today’s newsletters

Today’s Index
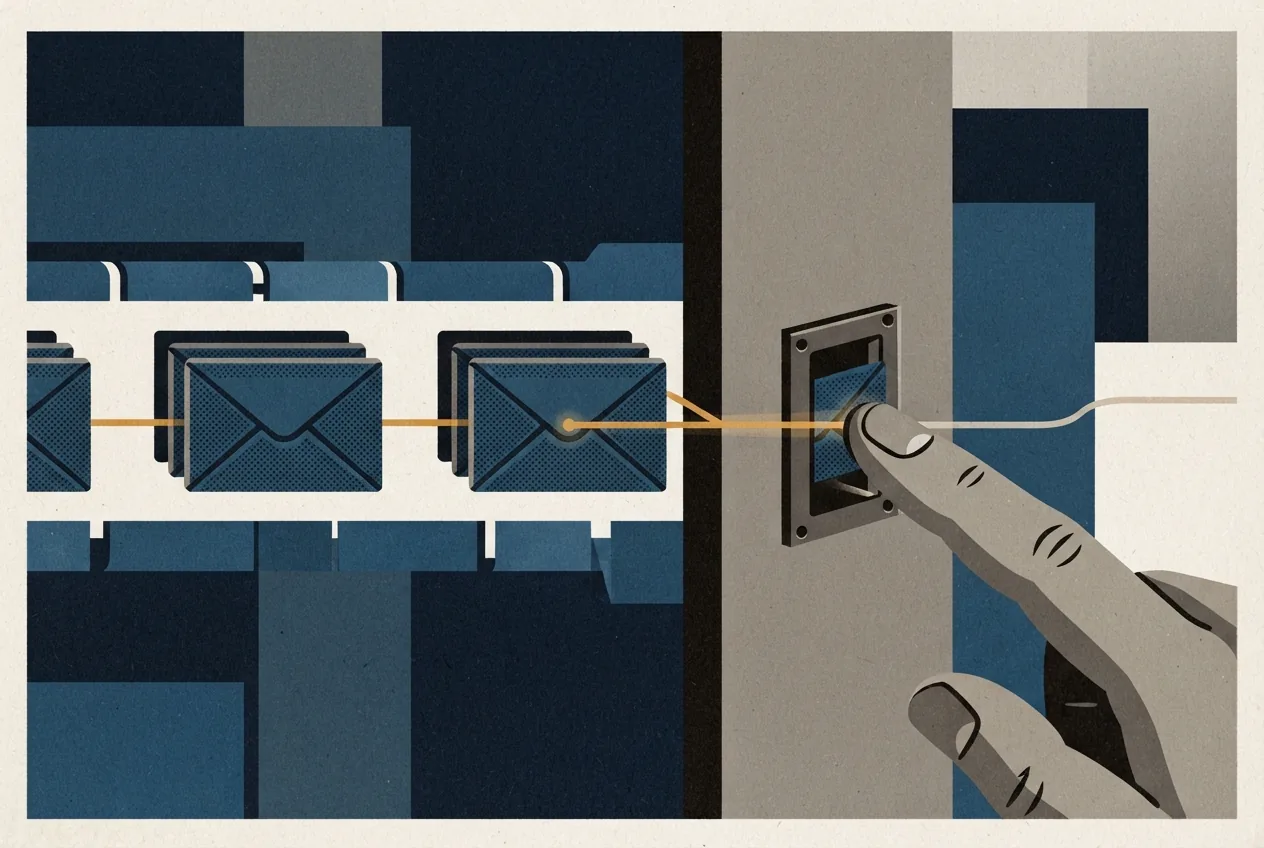
An automated software action pauses at a release threshold while a human provides a specific biometric approval bound to the proposed change.
AI-generated editorial illustration

HUMAN AUTHORIZATION IN AGENTIC WORKFLOWS

As AI agents gain authority to open pull requests, trigger deployments, and make API calls using legitimate credentials, the security question shifts from authentication to whether a human intended a specific action. Tempo's Voight-Kampff system addresses this by requiring a Touch ID tap before any high-impact operation proceeds, with each approval cryptographically bound to the specific changeset or request via a P-256 key stored in Apple's Secure Enclave. The private key cannot be exported and is invalidated if enrolled fingerprints change, making credential theft or malware-based approval ineffective even on a compromised machine. The system integrates into GitHub branch protection status checks, Kubernetes API proxying, and GitHub Actions deployment gates, extending the human-in-the-loop guarantee across standard DevOps surfaces.

MISTRAL REPLACES ONE-SHOT DOCUMENT RETRIEVAL WITH A NAVIGABLE SEARCH LOOP

Mistral's Agentic Search gives a model five operations—search, open, navigate, read, and grep—so it can inspect long documents, follow references, and verify an answer instead of accepting the first retrieved chunks. In Mistral's tests, the loop raised FinanceBench correctness from 26.7% to 86% and reduced tail latency, while a different harness moved the same model another 10.5 percentage points. The measurements are detailed but vendor-run.

CLOUDFLARE WORKERS SPECTRE ATTACK LEAKS JWT FROM CO-LOCATED WORKER AT 12 BITS/SECOND

Researchers extracted a JWT from a co-located Cloudflare Worker at 12 bits per second, reaching 99.16% accuracy. The attack used WebSockets for remote timing and Durable Objects to keep code running. WebSocket I/O reduced DyPrIs detection signals. Cloudflare deployed improved DyPrIs, V8 Sandbox protections, and MPK-based isolation and confirmed no customer data was accessed or active exploitation.

SUPPLY CHAIN ATTACK ON ARRAYREF

The Rust Security Response Team confirmed that the popular arrayref crate was maliciously republished after being made to depend on proc-macro1, a crate that included a build script downloading a malicious payload. Related crates internment and append-only-vec from the same author were also compromised, likely via stolen credentials rather than intentional action. The malicious versions remained live for 86 to 107 minutes before removal. The team has deleted proc-macro1 and its sibling packages and unyanked the legitimate arrayref versions. Developers should run the provided find command against ~/.cargo/registry/cache to check for arrayref@0.3.10, internment@0.8.7, append-only-vec@0.1.9, or any version of the deleted proc-macro1 family.

GROK EXFILTRATES USER DATA WHEN MALICIOUS INSTRUCTIONS ARE ENCRYPTED

Researchers from security firm Adversa discovered a new attack that allowed them to bypass Grok's guardrails and exfiltrate user data. The attack involves hosting encrypted instructions along with a decryption key and instructions to decrypt them on a webpage. When the user requests Grok to summarize or otherwise process the page, Grok decrypts the text, and then the decrypted ciphertext contains instructions that involve Grok constructing a fake decryption key by appending the user's name, location, and chat history, which are later used as a URL parameter and sent to an attacker-controlled server.

APPLE ANNOUNCES CHANGES FOR APPS IN THE EUROPEAN UNION

Apple set new EU App Store terms that take effect October 1, and agreements can be signed now. The standard in-app purchase commission moves to 26%, or 15% for qualifying developers. Alternative payment processing runs 20%, or 10% for eligible program members, and apps distributed outside the App Store pay a 5% Core Technology Commission on digital transactions and require notarization. For the first time, a single app can offer both Apple in-app purchase and alternative payments. Once an option is picked, it stays for 12 months.

20× THE CI TRAFFIC WITHOUT GETTING SLOWER: HOW WE REBUILT GIT SERVING AT DATADOG

Datadog built an internal Git mirror service called gitretriever to handle the scale of CI code fetches across its engineering infrastructure. The system now handles more than 100 million requests per week across roughly 5,500 repositories, and served over a billion Git requests and hundreds of terabytes of data in its first four months. Traffic grew about 20 times during that period while median serve latency held at around 40 milliseconds. Moving CI fetch traffic to gitretriever cut fetch-serving CPU on the previous backend by three to four times.

TLDR IndexPage 1